
Security, on every plan
Your website is attacked every day. We make sure it never notices.
Most hosts give you a padlock and hope. We put seven layers between attackers and your site, watch it around the clock with Skywatch, and tell you what we stopped in plain English.
- Known attackers blocked at the firewall
- 0+
- Layers of protection on every plan
- 0
- Threat feeds Skywatch checks against
- 0
- Passwords that can log in to our servers
- 0
Figures from our servers, October 2026.
Defence in depth
Seven layers between an attacker and your website.
If one layer misses something, the next one catches it. Scroll to follow an attack down through them.
-
Layer 01
Firewall and shared blocklist
Known attackers never reach your site. Our firewall drops traffic from 15,000+ addresses already caught attacking servers elsewhere, from a blocklist shared by thousands of servers worldwide and refreshed all day.
- CrowdSec community blocklist
- Dropped before it reaches the web server
-
Layer 02
Behaviour detection
Someone guessing passwords, probing admin pages or scanning for known vulnerabilities is spotted from the logs and banned automatically, across the web server, email, SSH and databases.
- Brute-force and probe detection
- Automatic bans
-
Layer 03
Web application firewall
Every request to your site is checked against the OWASP Core Rule Set, the industry-standard rules for stopping SQL injection, cross-site scripting, file inclusion and malicious bots. It runs in blocking mode.
- OWASP Core Rule Set 4
- Blocking, not just logging
-
Layer 04
Skywatch threat intelligence
Skywatch checks the addresses that touch your site against global threat feeds and flags attacks on your logins as they happen.
- AbuseIPDB
- AlienVault OTX
- Spamhaus
- Feodo Tracker
-
Layer 05
Malware and code integrity
New files are scanned for viruses the moment they are written. Every night Skywatch also reads every file your site serves, looking for web shells, card skimmers, hidden code and PHP hiding in upload folders.
- Real-time antivirus
- Nightly code sweep
- Reversible quarantine
-
Layer 06
A hardened server
HTTPS everywhere with strict security headers, server logins by encryption key only (no passwords to guess), each site in its own account, and security updates installed automatically every day.
- Key-only SSH
- TLS 1.2 and 1.3 only
- Daily security updates
- HSTS and CSP headers
-
Layer 07
Backups you can restore
Every site is backed up on its own schedule and the whole server every month, to separate storage away from the server over an encrypted link. If a backup fails, we are alerted within 15 minutes.
- Off-server storage
- Failure alerts
- Restore from the portal
What gets stopped
The attacks you will never hear about.
These are typical of what reaches any public website on an ordinary day, and the layer that deals with each one. You only hear from us when there is something worth knowing.
Check what is reaching your site- SQL injection in a search boxStopped by: Web application firewallBlocked
- 1,400 password guesses on wp-loginStopped by: Behaviour detectionBlocked
- Scanner probing /phpmyadmin and /.envStopped by: Behaviour detectionBlocked
- Traffic from a known botnet addressStopped by: Firewall blocklistBlocked
- Web shell uploaded through an old pluginStopped by: Real-time antivirusBlocked
- Card skimmer injected into checkout.jsStopped by: Nightly code sweepBlocked
- Spoofed email "from" your domainStopped by: Skywatch DNS checksBlocked
- Exploit attempt for a 2024 plugin CVEStopped by: Web application firewallBlocked
Skywatch
Our own security service, watching every site.
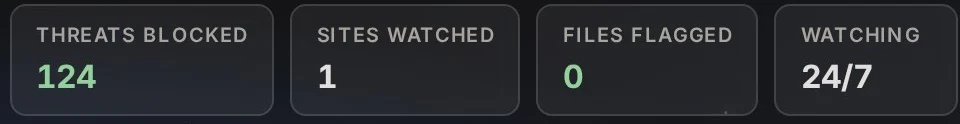
We built Skywatch because hosting dashboards show a green tick and little else. It works through a queue of checks every five minutes, sweeps every site's code every night, and writes a monthly security report for each site that a non-technical owner can read in two minutes.
- One-click Safe Repair for common weaknesses, and every fix can be undone
- Suspicious files quarantined, not deleted, so nothing is lost by mistake
- A security score for each site, explained line by line in your portal

Is the website hardened?
Security headers, cookies, exposed files and the SSL certificate, probed from outside.
Is the code clean?
Every file read for malware signatures, syntax errors and code that will break on the next PHP update.
Can someone send email as you?
SPF, DKIM, DMARC and CAA records checked, so nobody can spoof your domain.
Is anyone attacking it right now?
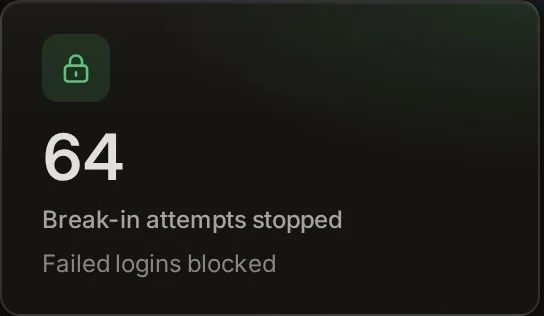
Login brute force, firewall blocks, file changes and threat-feed matches, as they happen.
If the worst happens
A plan, not a panic. Four steps, every time.
- 01
Detect
Skywatch and the firewall flag the problem, often within minutes, day or night.
- 02
Contain
The attacker is blocked and any malicious file is quarantined before it can spread.
- 03
Repair
We fix the weakness or restore a clean backup, then close the way they got in.
- 04
Explain
You get a plain-English account of what happened and what we changed.
Why it matters
Cheap hosting is only cheap until it isn't.
A hacked site can mean lost sales, a Google warning on your listing and your email marked as spam. This is the difference our layers make.
Is security really included on the cheapest plan?
Yes. Every layer on this page protects every site we host, from Starter up. The Skywatch bolt-on on Starter only adds the dashboard and monthly report in your portal; the protection itself is already there.
What happens if my site does get hacked?
We contain it first: the attacker is blocked and any malicious file is quarantined, which can be undone if it turns out to be harmless. Then we repair the site or restore it from a clean backup, find how they got in and close it, and tell you in plain English what happened.
Can you move my existing site over and check it?
Yes. Ask for a free security check and we will scan your current site for malware, outdated software, weak headers and email spoofing risks, and send you the results whether or not you move to us.
Who can see my data?
Only our team, and only to look after your site. Each client site runs in its own account on the server, our own logins use encryption keys rather than passwords, and your portal is protected by its own login.
Do you protect email as well as the website?
Skywatch checks your domain's SPF, DKIM and DMARC records so criminals cannot easily send email pretending to be you, and our server watches its own mail service for abuse and password guessing.
Get in touch
Let's build something brilliant.
Tell us about your project and we'll get back to you within 1 business day. Free consultation, no commitment.
- Emailcontact-us@customlaunch.co.uk
- ResponseWithin 1 business day
- Based inUnited Kingdom
Thanks, message received.
We'll be in touch within 1 business day.